Security
Built for financial data that matters. Protect access, isolate sensitive work, and keep the controls around your financial environment clear as Oculon scales with your team.
Access controls from day one
View, Edit and Manage across private assets, teams, workspaces, agents, automations and dashboards
Only the access each person needs, nothing more
Connect Oculon to your identity provider with SSO/SAML and manage user provisioning through SCIM.
Controls at every layer
Independently certified
SOC 2 Type II
Independent audit of Oculon’s security controls, tested over time.
Certified
ISO 27001
Certified information security management system.
Certified
GDPR
Personal data handled in line with EU data-protection requirements.
Certified
Security built into how Oculon is developed
Security is built into Oculon’s development and operations, from code review and vulnerability management to monitoring and incident response.
Give enterprise teams the controls they expect
Single sign-on
SSO with SAML through your identity provider.
Provisioning
SCIM user provisioning and deprovisioning.
Role-based access
View, Edit and Manage permissions across every asset.
Audit history
Event history with retention and export.
Encryption
Customer data encrypted in transit and at rest.
AI controls
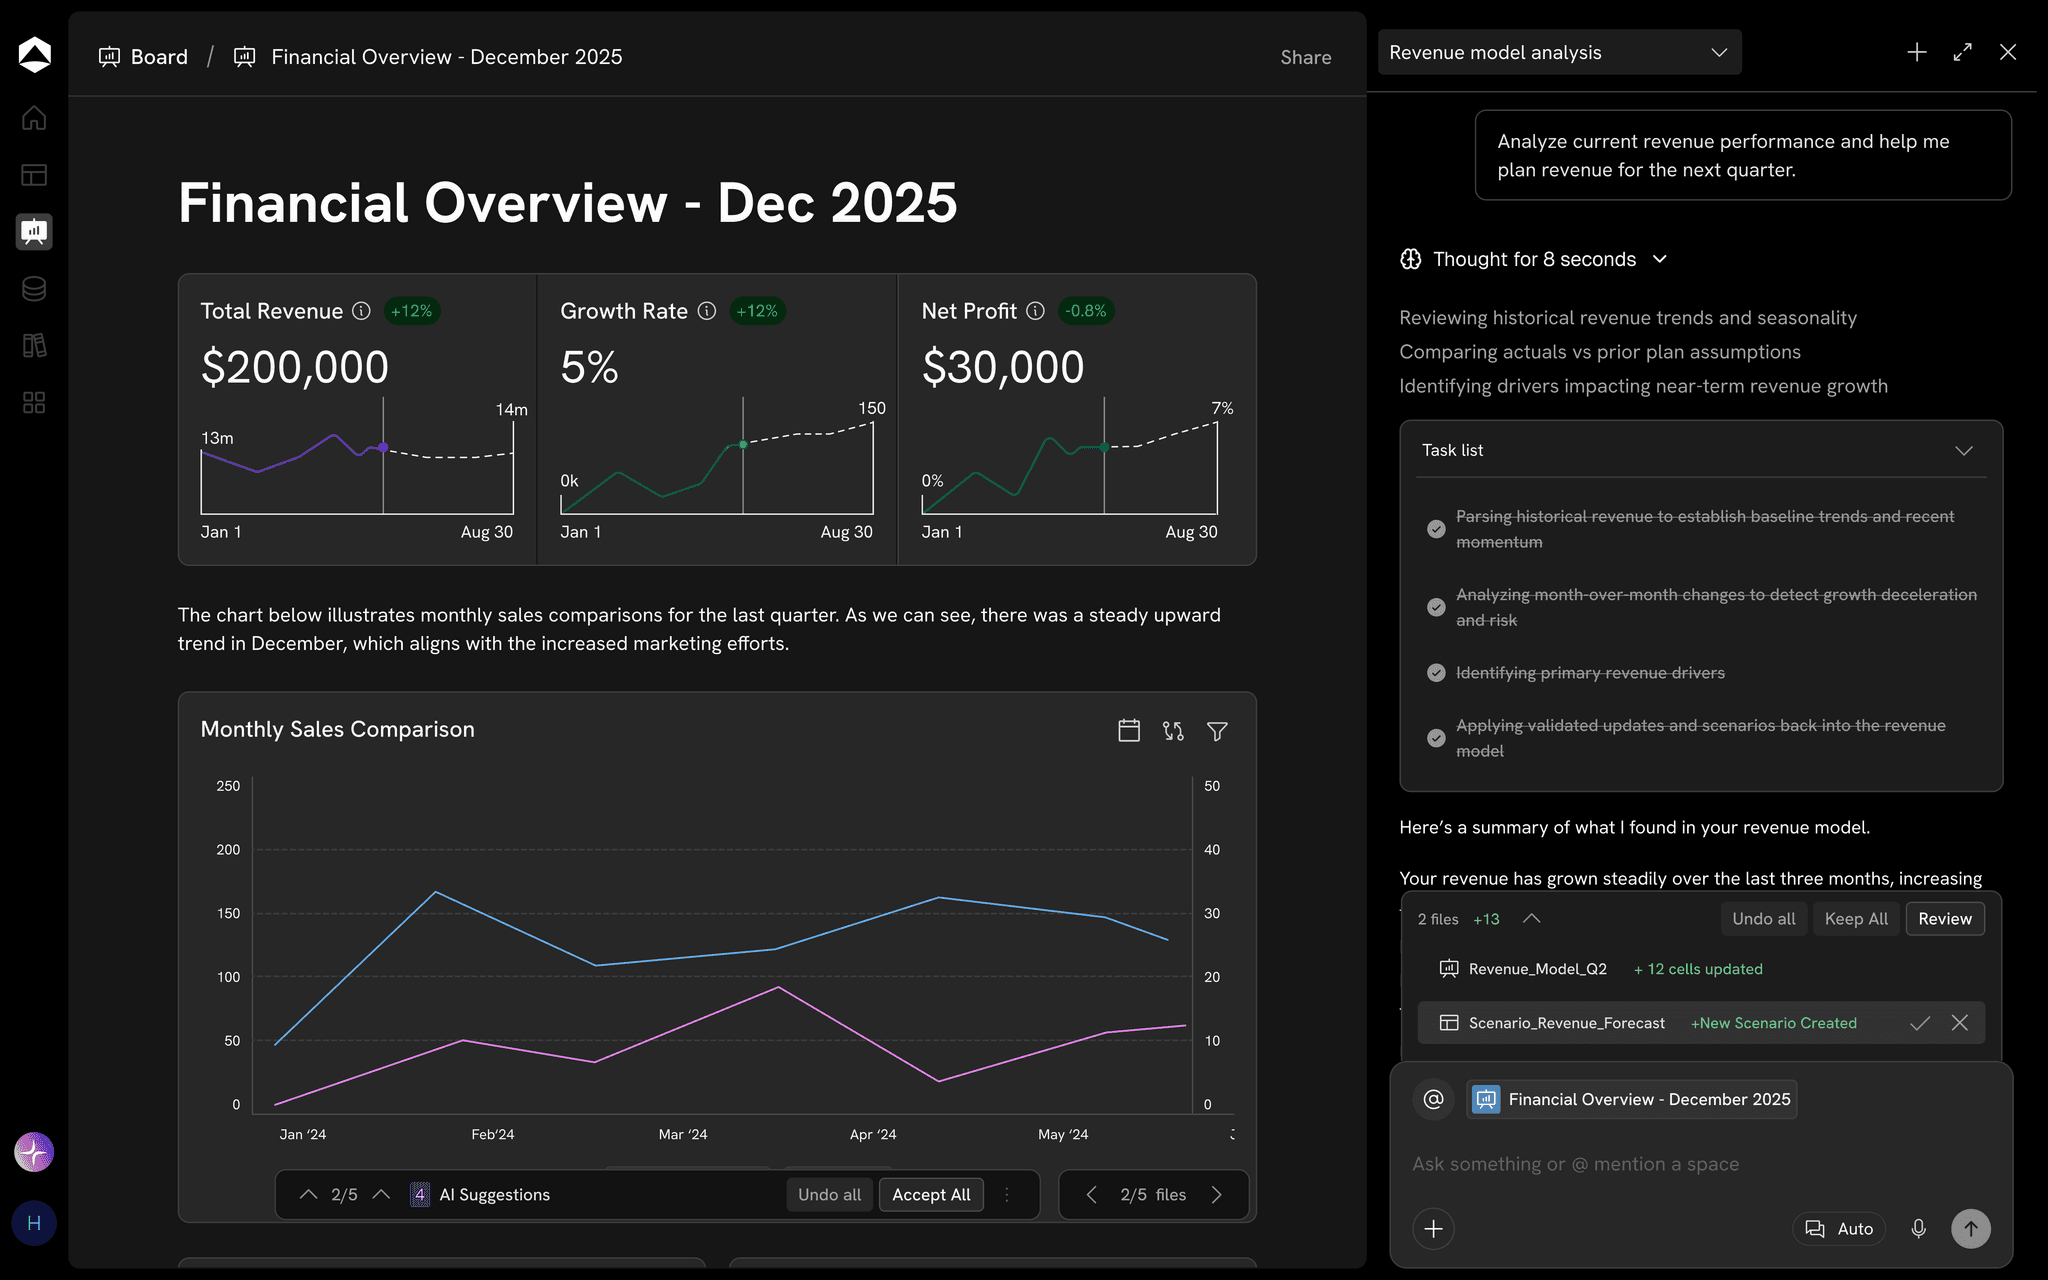
Sandboxes, human approval and memory controls.
Data residency
Custom residency options for your data.
Monitoring
Security logging and detection.
Business continuity
Backups and tested recovery objectives.
Security documents
Everything your security and procurement teams need, in one place: certifications, security reports, policies, subprocessors, privacy documentation and questionnaires.
Certifications
Security reports
Policies
Subprocessors
Privacy documentation
Questionnaires & procurement
Frequently asked questions
Oculon supports View, Edit, and Manage permissions across different parts of the workspace.
Yes. Oculon supports separate workspaces for different organizational or operating environments.
Yes. Oculon records who acted, what changed, when, and where.
AI changes can be isolated in a sandbox, reviewed, approved, rejected, revised, and rolled back.
Oculon is SOC 2 Type II and ISO 27001 certified, and GDPR compliant.
Yes. Oculon encrypts customer data in transit and at rest using industry-standard encryption.
Customer financial data remains isolated to your environment and is not used to train shared foundation models. AI providers and subprocessors are reviewed against Oculon’s security and data-protection requirements.